Log Analysis Challenge 2 - Cloudy, with a Trail of Logs
Prompt
Cirrus Solutions maintains detailed activity logs of their compute resources. Liber8tion is suspected of probing these resources - can you trace the events to answer the questions below?
Answers
Q1 (10 pts) - What was the first EC2 action performed in these logs?
DescribeInstances
Q2 (15 pts) - How many unique users are in these logs?
5
Q3 (15 pts) - How many minutes elapsed between the first and last event (rounded to the nearest integer)?
N/A
Q4 (15 pts) - Which instance ID appears most frequently in these logs?
N/A
Q5 (15 pts) - Which user terminated the most EC2 instances?
N/A
Q6 (15 pts) - Which IP address was used by more than one user?
N/A
Q7 (15 pts) - Which user does not have MFA enabled for all sessions?
N/A
Steps I Took
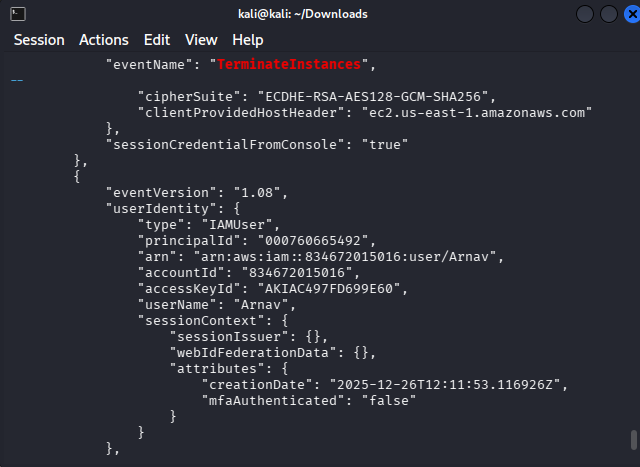
Q1 — I started by collecting the main fields that looked useful for the rest of the challenge:
eventTime
eventName
userIdentity.userName
sourceIPAddress
requestParameters.instancesSet.items[].instanceId
userIdentity.sessionContext.attributes.mfaAuthenticated
I used those fields to look for the first EC2 event and found DescribeInstances.
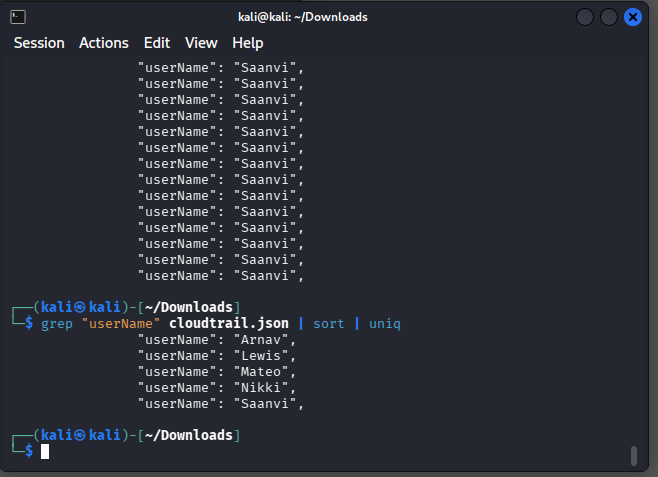
Q2 — I pulled the username field and performed a grep search with it.
Q3 — I used tail on the last 50 lines to get the final event time, then head on the first 25 lines to get the starting event time.
2025-12-26T12:04:17.116926Z”,
2025-12-26T17:45:25.116926Z”,
Then I subtracted the two timestamps.
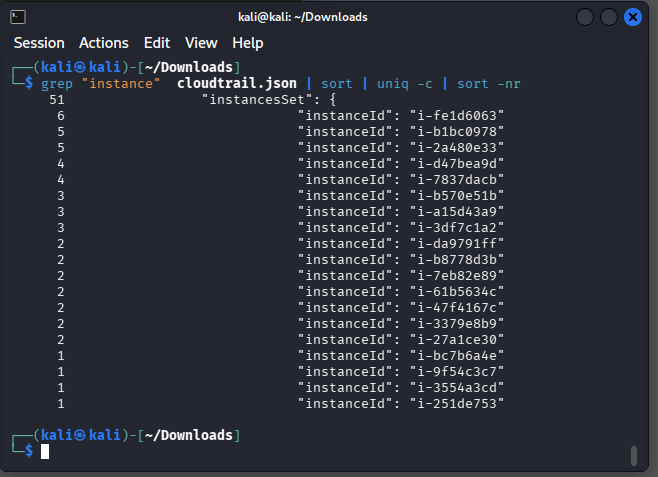
Q4 — I started by trying several grep commands until I got a useful response. After searching for instance, I began piping the output until I isolated the most common instance ID.
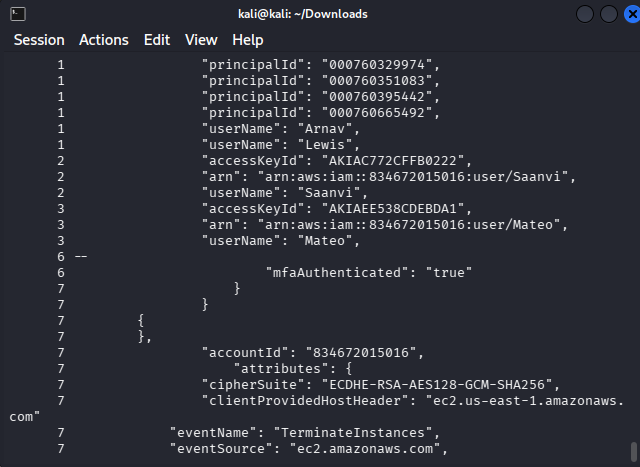
Q5 — I started by finding a string that returned a useful grep result.
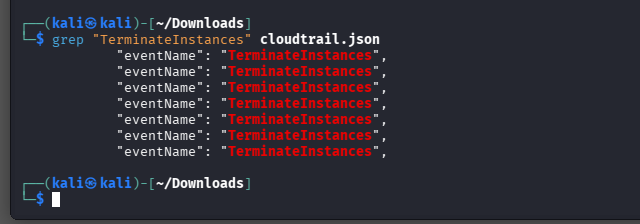
I kept increasing the -B value until the username appeared consistently, and I ended up using 25.
Then I sorted the results and checked the unique lines. The output included more than just usernames, but it still made the correct user clear.
Q6 — I used the -B argument again for this one.
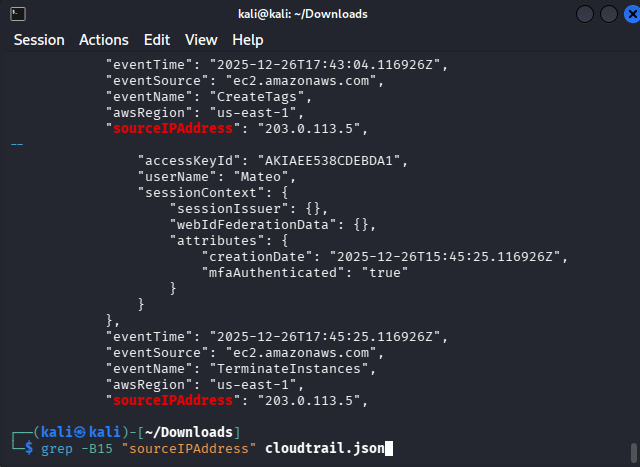
I counted the lines between the source IP and the username fields, then searched until I found two users sharing the same IP address.
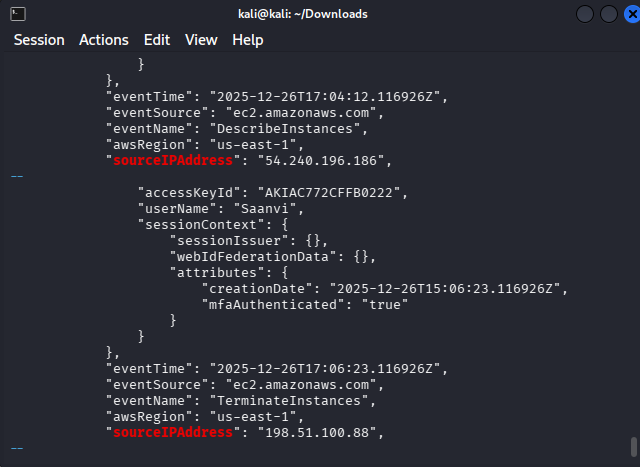
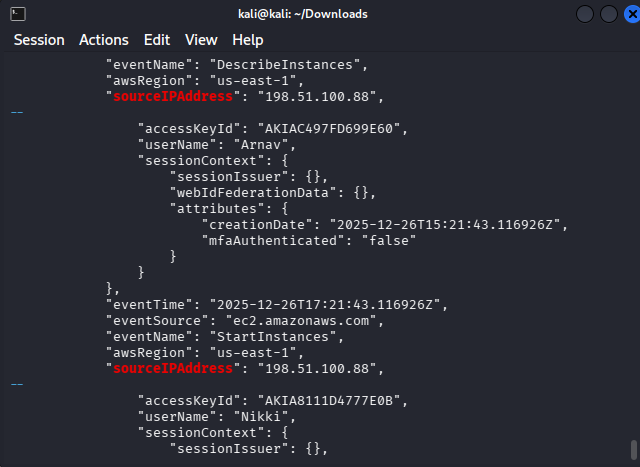
Q7 — I reused the same approach from Q5, but simplified it to:
grep -B25 "TerminateInstances" cloudtrail.json
I used that because it still showed the information I needed without adding extra complexity.