Enumeration & Exploitation Challenge 3 - Liber8eze
Prompt
We found one of Liber8tion’s servers with a binary called liber8eze on it. The server has a flag at /flag.txt. Can you use the binary to read the flag?
Answers
Q1 (10 pts) - What language is this binary written in?
Rust
Q2 (15 pts) - What permission bit is set on the binary that runs it with elevated privileges?
setuid
Q3 (15 pts) - What environment variable can be used to control command execution?
LIBER8_CHANGE_CMD
Q4 (15 pts) - What shell is used to execute the injected command?
sh
Q5 (20 pts) - What libc function is called to preserve privileges before executing the shell command?
setreuid
Q6 (25 pts) - What is the flag?
SKY-RUST-3331
Steps I Took
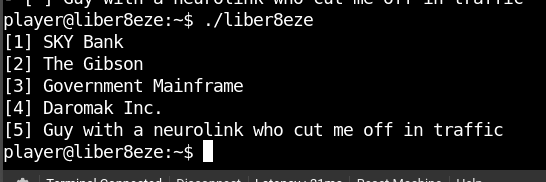
Started by running the program in the NCL Terminal
Opened the file up with Ghidra Saw this in the data types
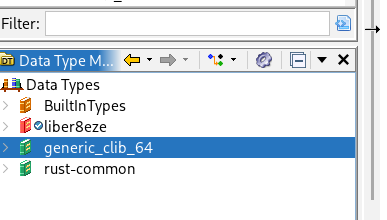
Told me that it was written in rust
I spent a lot of time on this and was very focused, so I did not end up keeping that accurate of notes
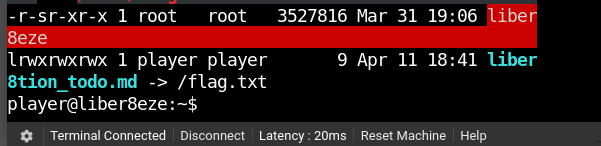
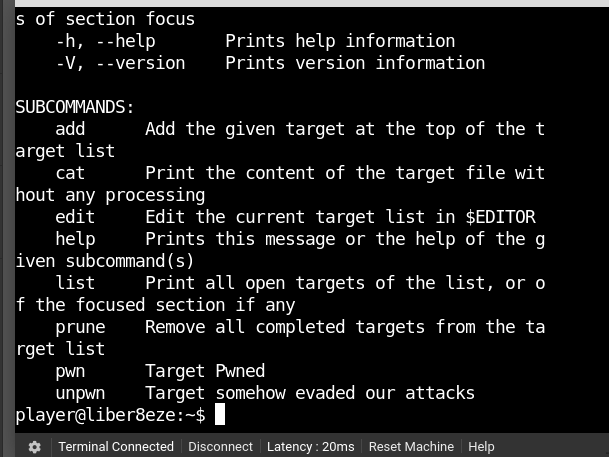
The binary was able to execute commands as root. This is the help section of the binary:
This was the point where I stalled, so I used ChatGPT to help me think through possible next steps. It did not provide the flag directly, but it suggested trying this command: strings -a ./liber8eze | grep LIBER8_
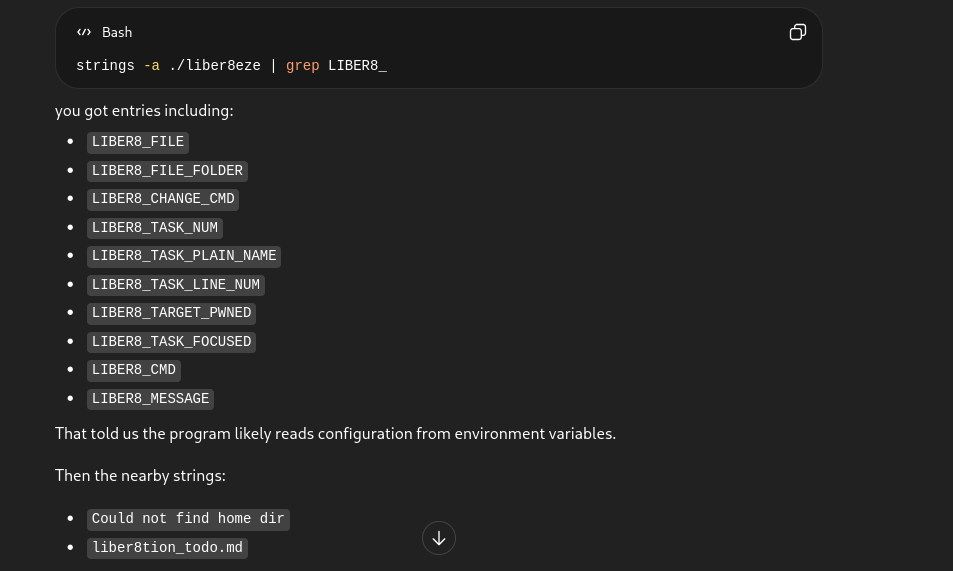
I spent some time testing different ideas based on those strings.
I eventually came back to this command: strings -a ./liber8eze | grep LIBER8_ That returned the flag.
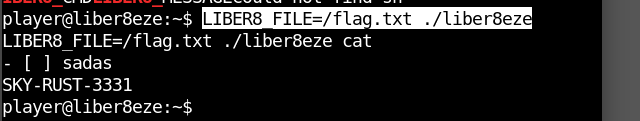
My interpretation was that LIBER8_FILE controls what gets opened when the binary runs, although I was less confident about that part of the analysis than the rest of the challenge.